Skip to content

It Audit & Testing

Image (CoNetrix Security)-1

Understand your risk.
Strengthen your security.

CoNetrix Security helps organizations identify risk, validate security controls, and strengthen their IT security through independent IT audits, penetration testing, security assessments, and other cybersecurity services.
10,000+
IT Audits & Security Engagements
650+
Financial Institutions Served
25+ Years
Helping Financial Institutions Strengthen Security
150+ Certifications
CISSP, CISA, CISM, and more
sec-transp-locks-cropped

Independent Testing

IT Audits & Security Testing for Regulated Industries

Financial institutions, healthcare organizations, and other regulated industries face unique security and compliance challenges. CoNetrix Security provides IT audits, penetration testing, VISO, and other security services to help you identify risks and strengthen your IT security controls.
Our Security Services

Independent IT Audits & Security Testing

Every organization has different security requirements. CoNetrix Security delivers independent testing and consulting services tailored to your organization's needs.

IT Audit & Vulnerability Assessment

Evaluate your IT controls, policies, and infrastructure through a risk-based audit aligned with FFIEC, FDIC, OCC, NCUA, and other regulatory guidance.

Learn More →

Penetration 

Testing

Simulate real-world attacks to identify vulnerabilities before they can be exploited, including external and internal penetration testing.

Learn More →

Network Security Assessment

Review your network architecture, security controls, and operational practices to identify risks and strengthen the overall security of your IT environment.

Learn More →

Cloud Security Assessment

Evaluate your Azure cloud security configurations to identify risks, strengthen security controls, and support compliance objectives.

Learn More →

Internal Vulnerability Assessment

Identify vulnerabilities across your internal network through automated scanning and technical analysis of systems, configurations, and security controls.

Learn More →

Microsoft 365 Assessment

Evaluate your Microsoft 365 tenant’s security settings to uncover configuration gaps and strengthen access and data protection.

Learn More →

What to Expect

First, we learn your business. Then our experts get to work.

Tandem-Audit-Findings

Powered by Tandem

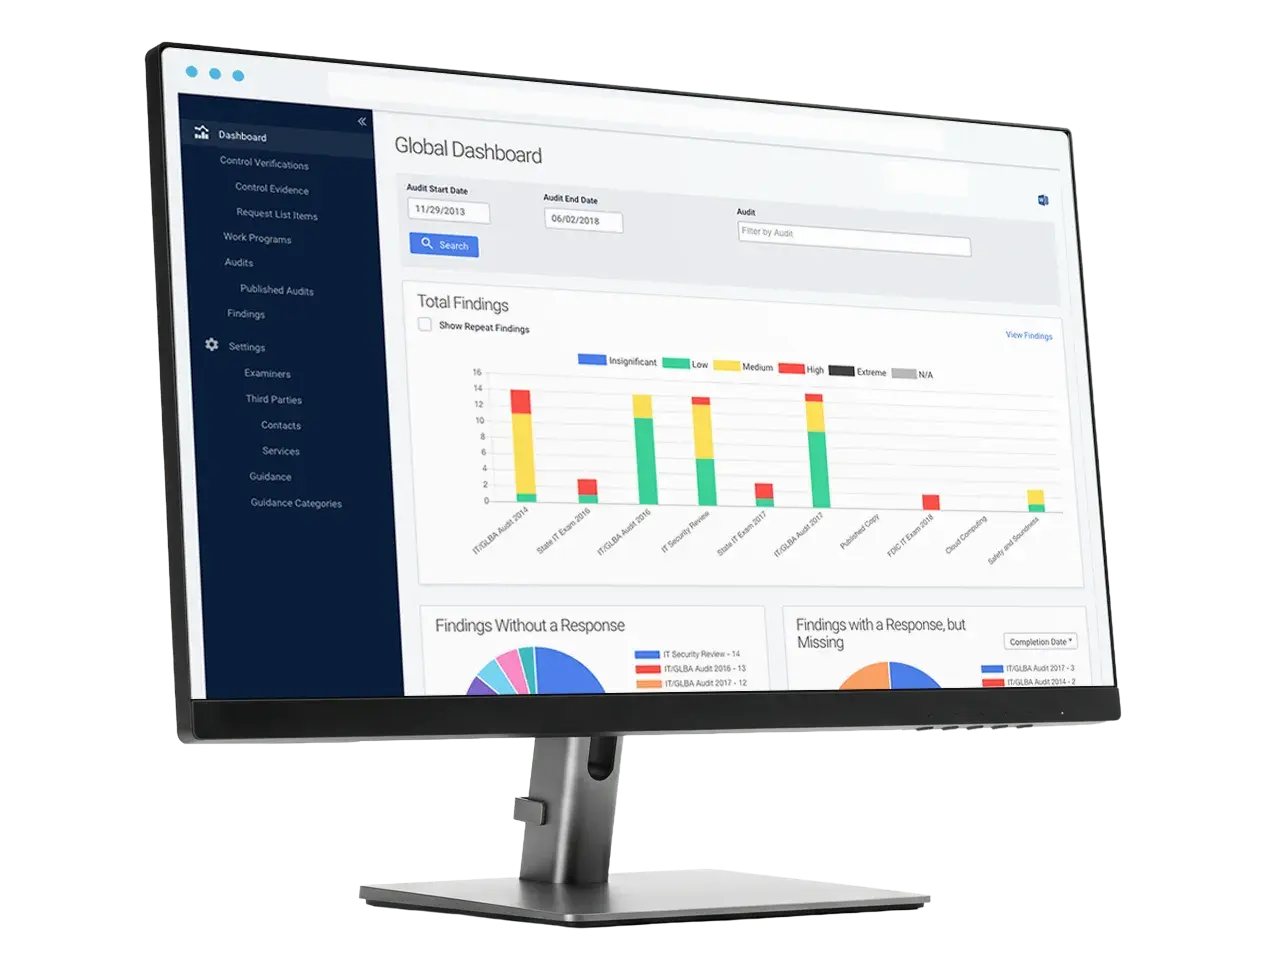
Tandem’s Audit Management Software Included

With each audit engagement, customers get access to Tandem, our audit management platform built to help regulated organizations coordinate documentation, manage findings, and stay prepared between audits.
  • Audit request list management
  • Centralized audit documentation
  • Finding & remediation tracking
  • Audit-ready reporting
SECArrowUp

We believe every finding is an opportunity to improve.

Our job isn't to overwhelm your team with technical jargon or a list of problems. We explain what we found, why it matters, and how to address it, providing practical guidance and clear priorities every step of the way. By the time we leave, you'll have a clear understanding of your results and a plan you can confidently put into action.

Get Started

Let's start with a conversation.

Tell us about your organization, your goals, and any upcoming regulatory requirements. We'll help you identify the security services that best fit your needs and answer any questions along the way.